Posts

How hundreds of websites are exposing their sensitive data and risking their user's privacy
Image
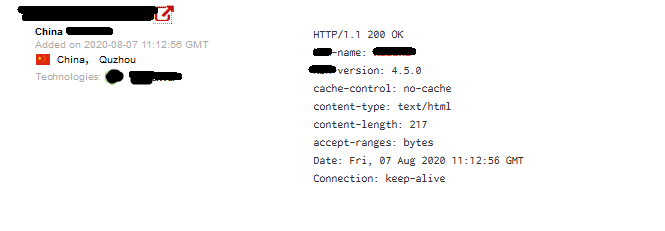
    The Purpose of this article is to show how some websites are exposing their sensitive data and risking their user's privacy. Recently some reports came out how some websites are exposing their kibana Instances due to misconfigure ElasticSearch Database so I decided to dig deeper to see how bad it can go . In this post I will show you how easily a blackhat guy could have compromised a site, its databse, it's user's personal information. To do this one can go to shodan.io and enter kibana port:5601 country:"US" org:"Amazon.com" in the search query   Above 5601 is the port number that you access kibana through the US is the country code for the country you want to access and Amazon.com is the services you want to discover like Azure, Google cloud, Digital Ocean, etc.   On searching above query i got 2.6k results    I checked on a random server     Below we can see a user (name hidden) logs. One can also see other details like name, address. ...
OSINT technique for information gathering and Background Verification

Image
We will see osint way to gather online info about the target. In this post I will use various open source tools and technique for passive information gathering. Lets assume our target is shaquib izhar. All we have is this name and we need to find as much information about him as possible. We will start with simple Google Dorking. My first query will be “shaquib izhar” this will give all websites, URL where this specific name is available. Let’s see what result we get from this search. We got his twitter profile, quora and other social media accounts registered with this name. There’s also a link of about.me profile on Google search associated with this name. Let's go to that link and see if we can gather some another information. Below we can see there’s a connect with me LinkedIn link of his profile N ow, because I am using a VPN, whenever I follow that LinkedIn profile link, it is asking me to login to view that profile. And we can’t login because it can notify the user tha...

Pwning a person using basic Red team techniques and social engineering Attack

Image
This time I have decided not to phish the user’s password instead I will pwn his device. I will generate persistent spyware which will log target’s keystrokes, screenshots and webcam snapshots (if the user has a webcam) STEP1: Gathering information This step is about to gather information about my target, as my target does not has any computers knowledge coming from arts medium (from his Facebook profile) it is easy to phish him, but first I am going to gather information about what OS is he using, what version of the operating system he is running. So to do this I created an IP tracer that will gather his user-agent info, his current location(if he gives access), what device is he using. When he opens the link I got all the information I required to prepare my attack and saved everything on the log file. Below is a snapshot of his device details.   Now I know he is using windows 10 operating system so I can prepare my spyware keeping this information...